Our wallet review process
We examine wallets starting at the code level and continue all the way up to the finished app that lives on your device. Provided below is an outline of each of these steps along with security tips for you and general test results.
Passed all 10 tests
We answered the following questions in this order:
The answer is "yes".
If the answer were "no", we would mark it as "Fake" and the following would apply:
The answer is "no". We marked it as "Fake".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Fake" and the following would apply:
The bigger wallets often get imitated by scammers that abuse the reputation of the product by imitating its name, logo or both.
Imitating a competitor is a huge red flag and we urge you to not put any money into this product!
The answer is "yes".
If the answer were "no", we would mark it as "Announced but never delivered" and the following would apply:
The answer is "no". We marked it as "Announced but never delivered".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Announced but never delivered" and the following would apply:
Some products are promoted with great fund raising, marketing and ICOs, to disappear from one day to the other a week later or they are one-man side projects that get refined for months or even years to still never materialize in an actual product. Regardless, those are projects we consider “vaporware”.
The answer is "yes".
If the answer were "no", we would mark it as "Un-Released" and the following would apply:
The answer is "no". We marked it as "Un-Released".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Un-Released" and the following would apply:
We focus on products that have the biggest impact if things go wrong and while pre-sales sometimes reach many thousands to buy into promises that never materialize, the damage is limited and there would be little definite to be said about an unreleased product anyway.
If you find a product in this category that was released meanwhile, please contact us to do a proper review!
The answer is "yes".
If the answer were "no", we would mark it as "Not a wallet" and the following would apply:
The answer is "no". We marked it as "Not a wallet".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Not a wallet" and the following would apply:
If it’s called “wallet” but is actually only a portfolio tracker, we don’t look any deeper, assuming it is not meant to control funds. What has no funds, can’t lose your coins. It might still leak your financial history!
If you can buy Bitcoins with this app but only into another wallet, it’s not a wallet itself.
The answer is "yes".
If the answer were "no", we would mark it as "A wallet but not for Bitcoin" and the following would apply:
The answer is "no". We marked it as "A wallet but not for Bitcoin".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "A wallet but not for Bitcoin" and the following would apply:
At this point we only look into wallets that at least also support BTC.
The answer is "yes".
If the answer were "no", we would mark it as "Provided private keys" and the following would apply:
The answer is "no". We marked it as "Provided private keys".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Provided private keys" and the following would apply:
The best hardware wallet cannot guarantee that the provider deleted the keys if the private keys were put onto the device by them in the first place.
There is no way of knowing if the provider took a copy in the process. If they did, all funds controlled by those devices are potentially also under the control of the provider and could be moved out of the client’s control at any time at the provider’s discretion.
The product cannot be independently verified. If the provider puts your funds at risk on purpose or by accident, you will probably not know about the issue before people start losing money. If the provider is more criminally inclined he might have collected all the backups of all the wallets, ready to be emptied at the press of a button. The product might have a formidable track record but out of distress or change in management turns out to be evil from some point on, with nobody outside ever knowing before it is too late. The answer is "yes".
If the answer were "no", we would mark it as "Leaks Keys" and the following would apply:
The answer is "no". We marked it as "Leaks Keys".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Leaks Keys" and the following would apply:
Some people claim their paper wallet is a hardware wallet. Others use RFID chips with the private keys on them. A very crucial drawback of those systems is that in order to send a transaction, the private key has to be brought onto a different system that doesn’t necessarily share all the desired aspects of a hardware wallet.
Paper wallets need to be printed, exposing the keys to the PC and the printer even before sending funds to it.
Simple RFID based devices can’t sign transactions - they share the keys with whoever asked to use them for whatever they please.
There are even products that are perfectly capable of working in an air-gapped fashion but they still expose the keys to connected devices.
This verdict is reserved for key leakage under normal operation and does not apply to devices where a hack is known to be possible with special hardware.
The product cannot be independently verified. If the provider puts your funds at risk on purpose or by accident, you will probably not know about the issue before people start losing money. If the provider is more criminally inclined he might have collected all the backups of all the wallets, ready to be emptied at the press of a button. The product might have a formidable track record but out of distress or change in management turns out to be evil from some point on, with nobody outside ever knowing before it is too late. The answer is "yes".
If the answer were "no", we would mark it as "Bad Interface" and the following would apply:
The answer is "no". We marked it as "Bad Interface".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Bad Interface" and the following would apply:
These are devices that might generate secure private key material, outside the reach of the provider but that do not have the means to let the user verify transactions on the device itself. This verdict includes screen-less smart cards or USB-dongles.
The wallet lacks either a screen or buttons or both. In consequence, crucial elements of approving transactions is being delegated to other hardware such as a general purpose PC or phone which defeats the purpose of a hardware wallet. For big exit scams, a companion app could always request two signatures - one for the coffee you are paying and a second to empty your wallet completely. The former could be broadcast while the latter only gets collected for later use.
Another consquence of a missing screen is that the user is faced with the dilemma of either not making a backup or having to pass the backup through an insecure device for display or storage.
The software of the device might be perfect but this device cannot be recommended due to this fundamental flaw.
The product cannot be independently verified. If the provider puts your funds at risk on purpose or by accident, you will probably not know about the issue before people start losing money. If the provider is more criminally inclined he might have collected all the backups of all the wallets, ready to be emptied at the press of a button. The product might have a formidable track record but out of distress or change in management turns out to be evil from some point on, with nobody outside ever knowing before it is too late. The answer is "yes".
If the answer were "no", we would mark it as "No source for current release found" and the following would apply:
The answer is "no". We marked it as "No source for current release found".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "No source for current release found" and the following would apply:
A wallet that claims to not give the provider the means to steal the users’ funds might actually be lying. In the spirit of “Don’t trust - verify!” you don’t want to take the provider at his word, but trust that people hunting for fame and bug bounties could actually find flaws and back-doors in the wallet so the provider doesn’t dare to put these in.
Back-doors and flaws are frequently found in closed source products but some remain hidden for years. And even in open source security software there might be catastrophic flaws undiscovered for years.
An evil wallet provider would certainly prefer not to publish the code, as hiding it makes audits orders of magnitude harder.
For your security, you thus want the code to be available for review.
If the wallet provider doesn’t share up to date code, our analysis stops there as the wallet could steal your funds at any time, and there is no protection except the provider’s word.
“Up to date” strictly means that any instance of the product being updated without the source code being updated counts as closed source. This puts the burden on the provider to always first release the source code before releasing the product’s update. This paragraph is a clarification to our rules following a little poll.
We are not concerned about the license as long as it allows us to perform our analysis. For a security audit, it is not necessary that the provider allows others to use their code for a competing wallet. You should still prefer actual open source licenses as a competing wallet won’t use the code without giving it careful scrutiny.
The product cannot be independently verified. If the provider puts your funds at risk on purpose or by accident, you will probably not know about the issue before people start losing money. If the provider is more criminally inclined he might have collected all the backups of all the wallets, ready to be emptied at the press of a button. The product might have a formidable track record but out of distress or change in management turns out to be evil from some point on, with nobody outside ever knowing before it is too late.Build Verifications
If you have a binary for a version that doesn't appear on the list, you can dropselect the file here to register it so somebody can verify its reproducibility:
Application information
Background
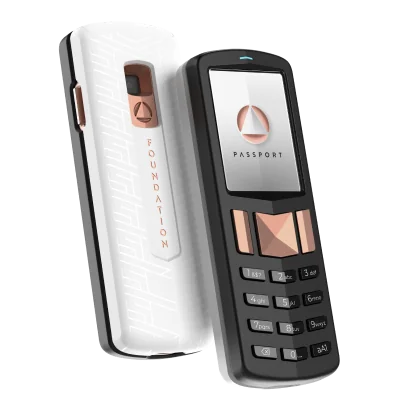
Foundation Passport is the next iteration for the
 Foundation Passport - Founder's Edition .
Product Description
It features the following specifications:
- Supported Cryptocurrencies: Bitcoin via PSBTs; best-in-class multisig experience.
- Supported Software Wallets: Bitcoin Core, BlueWallet, BTCPay, Casa, Electrum, Nunchuk, Simple Bitcoin Wallet, Sparrow, Specter, Wasabi, and other wallets supporting PSBTs via microSD or QR codes.
- Key Components: STM processor, Microchip 608a secure element, Omnivision Cameracube.
- Communication: Camera and microSD port. No USB data, no Bluetooth, no wireless communications of any kind.
- Power: 1200 mAh Lithium ion battery in Nokia BL-5C form factor (included with purchase).
- Security Features: Airgapped, easy passphrase entry, security lights, anti-phishing words, supply chain verification.
From Foundation’s Twitter account:
- 20% thinner design
- Standard form factor lithium-ion battery
- High resolution IPS color display bonded to ultra-hard glass
- STM processor, Microchip 608a secure element, Omnivision cameracube, and an avalanche noise source for entropy
- Physical power button
- Improved microSD slot
- Power only USB-C port
Passport now ships these accessories:
- Industrial-grade microSD card
- Removable lithium-ion battery
- microSD adapters for iOS and Android
- USB-C charging cable.
- Helps you securely and easily set up Passport.
- Keeps you up-to-date with firmware updates, no computer required!
- Provides quick and easy access to support resources.
- Let’s you send, receive, and “boost” bitcoin transactions.
Onboarding: Envoy guides the user through unboxing Passport and setting it up securely, no need for a computer
Security: Envoy primarily communicates with Passport via airgapped QR codes, ensuring that Passport is never directly connected to an online device.
Privacy: Envoy connects to Foundation’s server and Bitcoin node through Tor. Envoy offers the ability to connect to your own Bitcoin node, cutting out Foundation as the middleman.
Free and Open Source (FOSS)
The wallet’s source code is published under a license approved by the Open Source Initiative (OSI) — such as MIT, GPL, Apache, or AGPL — allowing anyone to inspect, modify, and redistribute it. This is a prerequisite for independent security audits and reproducible builds. Licenses that are merely “source available” but not OSI-approved (e.g., those with Commons Clause restrictions, commercial use prohibitions, or other non-free terms) do NOT qualify. Reproducible builds are not sufficient alone.
-
Transparency: Anyone can verify what the code does — including whether it contains backdoors, bugs, or privacy-violating behavior.
-
Community auditing: More reviewers means vulnerabilities are more likely to be found and fixed.
-
Forkability: If the project is abandoned or goes rogue, the community can fork and continue it.
FOSS alone does not guarantee security. The released binary must also be reproducible from the public source to ensure users are actually running the code that was audited.
Why we list it for this wallet
GNU General Public License v3.0 (GPLv3) or later
Source: GitHub README
Secure Elements
Secure Elements in Bitcoin wallets refer to dedicated hardware components designed to enhance security. These elements are specialized circuits or chips embedded in the device, providing a fortified environment for storing sensitive data such as private keys. Unlike standard storage, Secure Elements are resistant to tampering and physical attacks, making them an ideal choice for safeguarding cryptographic data and operations. The use of Secure Elements is crucial, especially in hardware and mobile wallets, where the risk of physical theft or tampering is a concern. These elements can effectively shield private keys from a wide range of attacks, including sophisticated ones like side-channel attacks. They ensure that private keys never leave the secure environment, even when signing transactions, offering a higher level of security compared to software-only solutions. While adding a significant layer of security, Secure Elements may pose challenges in terms of wallet recovery. In cases where the device is damaged or lost, retrieving the private keys can be more complex compared to wallets that solely use software-based security measures.
- Enhanced security against physical and sophisticated attacks
- Increased protection for private keys and sensitive data
- Peace of mind knowing that cryptographic operations are performed in a secure, isolated environment
Potential complexities in wallet recovery and dependency on specific hardware.
Why we list it for this wallet
Microchip 608a secure element
Source: Existing WalletScrutiny review
Camera for Secure Transactions
Camera functionality in Bitcoin hardware wallets, represents a significant advancement in wallet security and data transmission. These wallets use their built-in cameras to scan QR codes, enabling a secure and efficient method for data exchange and transaction signing. The camera-based approach is integral to maintaining an air-gapped environment, meaning the wallet does not rely on potentially vulnerable USB or Bluetooth connections for communication. The process involves creating an unsigned transaction as a QR code using a compatible wallet app. This QR code is then scanned by the hardware wallet’s camera. Inside the wallet, the transaction is securely signed using the stored private key. The signed transaction is subsequently displayed as a new QR code on the wallet, which can then be scanned back by the app to broadcast it to the blockchain network. This method of using a camera for QR code scanning and transmission ensures that the private keys remain solely within the hardware wallet, significantly bolstering security against remote attacks. It also enhances privacy, as the wallet does not directly connect to the internet or other devices, thereby reducing exposure to potential vulnerabilities.
- Enhanced security by maintaining an air-gapped environment
- Increased privacy as the wallet does not directly connect to the internet
- User-friendly transaction process with QR code scanning
Why we list it for this wallet
Communication: Camera and microSD port. No USB data, no Bluetooth, no wireless communications of any kind.
Source: Existing WalletScrutiny review
Air Gapped: App works without internet
Some apps mimic hardware wallets in that they don’t request permission to connect to the internet but instead they communicate through a companion app which has internet. That companion app might be on the same phone but with internet permission or it might be on a secondary phone such that the Air Gapped app can run on a phone that has no mobile or wifi internet configured at all.
Security: Splitting an app into a part that keeps the keys safe without access to leak them online and an app that has internet and all the rest can reduce the attack surface for the private keys. In theory this setup can be much more secure than the usual app that has both the private keys and internet access in one.
Why we list it for this wallet
Security: Envoy primarily communicates with Passport via airgapped QR codes, ensuring that Passport is never directly connected to an online device.
Source: Existing WalletScrutiny review
Multi Signature
Bitcoin allows to define addresses controlled by more than one private key. Two-of-three for example would mean that any two of a list of three private keys would be required to send coins from this address.
With keys from distinct devices or users, an attacker would have to compromise multiple devices or users at once. Multi signature thus allows to protect against one device catching a virus, one wallet having a backdoor (if the multi signature works across different providers’ wallets), one hardware wallet not being trusted (if hardware wallets can be used for multi signature), etc.
- There are no good standards yet for multi signature accounts. This might mean that an account that works with one provider’s wallet won’t load in any other wallet which can complicate recovery should that wallet go out of business.
- Using Multi Signature results in bigger and thus more expensive transactions.
- Using Multi Signature accounts makes it easier for blockchain analysis companies to follow the trail of a wallet.
- Multi Signature accounts require backups of additional descriptors, making financial loss from user error more likely.
Why we list it for this wallet
Supported Cryptocurrencies: Bitcoin via PSBTs; best-in-class multisig experience.
Source: Existing WalletScrutiny review
Custom Node Connection
The wallet can be configured to connect to a user-specified, independently operated Bitcoin node — such as Bitcoin Core, Electrum Server, or other compatible full node software — instead of the wallet provider’s default servers. The key requirement is that the node is clearly independent from the wallet vendor: a third-party node the user controls or trusts.
-
Privacy: Transaction queries go to your own node rather than a third-party server, so no provider learns your wallet addresses or balances.
-
Security: No risk of a provider lying about your balance or the state of the network.
-
Sovereignty: Full independence from wallet provider infrastructure.
- Requires running and maintaining your own Bitcoin node.
- More complex initial setup compared to using the provider’s default servers.
Why we list it for this wallet
Envoy offers the ability to connect to your own Bitcoin node, cutting out Foundation as the middleman.
Source: Existing WalletScrutiny review
Product page updated by Matthew Lamb, Leo Wandersleb, @sethforprivacy, Daniel Andrei R. Garcia, keraliss
Do your own research
In addition to reading our analysis, it is important to do your own checks. Before transferring any bitcoin to your wallet, look up reviews for the wallet you want to use. They should be easy to find. If they aren't, that itself is a reason to be extra careful.