Passed all 10 tests
We check each wallet from its code to the app on your device, asking these questions in order:
The answer is "yes".
If the answer were "no", we would mark it as "Fake" and the following would apply:
The answer is "no". We marked it as "Fake".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Fake" and the following would apply:
The bigger wallets often get imitated by scammers that abuse the reputation of the product by imitating its name, logo or both.
Imitating a competitor is a huge red flag and we urge you to not put any money into this product!
The answer is "yes".
If the answer were "no", we would mark it as "Announced but never delivered" and the following would apply:
The answer is "no". We marked it as "Announced but never delivered".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Announced but never delivered" and the following would apply:
Some products are promoted with great fund raising, marketing and ICOs, to disappear from one day to the other a week later or they are one-man side projects that get refined for months or even years to still never materialize in an actual product. Regardless, those are projects we consider “vaporware”.
The answer is "yes".
If the answer were "no", we would mark it as "Un-Released" and the following would apply:
The answer is "no". We marked it as "Un-Released".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Un-Released" and the following would apply:
We focus on products that have the biggest impact if things go wrong and while pre-sales sometimes reach many thousands to buy into promises that never materialize, the damage is limited and there would be little definite to be said about an unreleased product anyway.
If you find a product in this category that was released meanwhile, please contact us to do a proper review!
The answer is "yes".
If the answer were "no", we would mark it as "Not a wallet" and the following would apply:
The answer is "no". We marked it as "Not a wallet".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Not a wallet" and the following would apply:
If it’s called “wallet” but is actually only a portfolio tracker, we don’t look any deeper, assuming it is not meant to control funds. What has no funds, can’t lose your coins. It might still leak your financial history!
If you can buy Bitcoins with this app but only into another wallet, it’s not a wallet itself.
The same goes for off-ramps that hold no balance at all: bitcoin (or gift cards) go in and fiat goes straight out to your bank. An off-ramp that keeps your fiat until you cash out is a wallet, just not for Bitcoin. One that keeps a bitcoin balance you can’t send out is ‘Can’t send or receive bitcoins’.
The answer is "yes".
If the answer were "no", we would mark it as "A wallet but not for Bitcoin" and the following would apply:
The answer is "no". We marked it as "A wallet but not for Bitcoin".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "A wallet but not for Bitcoin" and the following would apply:
At this point we only look into wallets that at least also support BTC.
A product that can send and receive other coins but only tracks Bitcoin addresses read-only is a wallet, just not for Bitcoin, so it gets this verdict. ‘Not a wallet’ is for products that hold no coins at all, such as pure portfolio trackers.
The same goes for off-ramps that credit your bitcoin to a fiat balance you later cash out: the app holds your money, but not as bitcoin.
The answer is "yes".
If the answer were "no", we would mark it as "Provided private keys" and the following would apply:
The answer is "no". We marked it as "Provided private keys".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Provided private keys" and the following would apply:
The best hardware wallet cannot guarantee that the provider deleted the keys if the private keys were put onto the device by them in the first place.
There is no way of knowing if the provider took a copy in the process. If they did, all funds controlled by those devices are potentially also under the control of the provider and could be moved out of the client’s control at any time at the provider’s discretion.
The product cannot be independently verified. If the provider puts your funds at risk on purpose or by accident, you will probably not know about the issue before people start losing money. If the provider is more criminally inclined he might have collected all the backups of all the wallets, ready to be emptied at the press of a button. The product might have a formidable track record but out of distress or change in management turns out to be evil from some point on, with nobody outside ever knowing before it is too late. The answer is "yes".
If the answer were "no", we would mark it as "Leaks Keys" and the following would apply:
The answer is "no". We marked it as "Leaks Keys".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Leaks Keys" and the following would apply:
Some people claim their paper wallet is a hardware wallet. Others use RFID chips with the private keys on them. A very crucial drawback of those systems is that in order to send a transaction, the private key has to be brought onto a different system that doesn’t necessarily share all the desired aspects of a hardware wallet.
Paper wallets need to be printed, exposing the keys to the PC and the printer even before sending funds to it.
Simple RFID based devices can’t sign transactions - they share the keys with whoever asked to use them for whatever they please.
There are even products that are perfectly capable of working in an air-gapped fashion but they still expose the keys to connected devices.
This verdict is reserved for key leakage under normal operation and does not apply to devices where a hack is known to be possible with special hardware.
The product cannot be independently verified. If the provider puts your funds at risk on purpose or by accident, you will probably not know about the issue before people start losing money. If the provider is more criminally inclined he might have collected all the backups of all the wallets, ready to be emptied at the press of a button. The product might have a formidable track record but out of distress or change in management turns out to be evil from some point on, with nobody outside ever knowing before it is too late. The answer is "yes".
If the answer were "no", we would mark it as "Bad Interface" and the following would apply:
The answer is "no". We marked it as "Bad Interface".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Bad Interface" and the following would apply:
These are devices that might generate secure private key material, outside the reach of the provider but that do not have the means to let the user verify transactions on the device itself. This verdict includes screen-less smart cards or USB-dongles.
The wallet lacks either a screen or buttons or both. In consequence, crucial elements of approving transactions is being delegated to other hardware such as a general purpose PC or phone which defeats the purpose of a hardware wallet. For big exit scams, a companion app could always request two signatures - one for the coffee you are paying and a second to empty your wallet completely. The former could be broadcast while the latter only gets collected for later use.
Another consquence of a missing screen is that the user is faced with the dilemma of either not making a backup or having to pass the backup through an insecure device for display or storage.
The software of the device might be perfect but this device cannot be recommended due to this fundamental flaw.
The product cannot be independently verified. If the provider puts your funds at risk on purpose or by accident, you will probably not know about the issue before people start losing money. If the provider is more criminally inclined he might have collected all the backups of all the wallets, ready to be emptied at the press of a button. The product might have a formidable track record but out of distress or change in management turns out to be evil from some point on, with nobody outside ever knowing before it is too late. The answer is "yes".
If the answer were "no", we would mark it as "No source for current release found" and the following would apply:
The answer is "no". We marked it as "No source for current release found".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "No source for current release found" and the following would apply:
A wallet that claims to not give the provider the means to steal the users’ funds might actually be lying. In the spirit of “Don’t trust - verify!” you don’t want to take the provider at his word, but trust that people hunting for fame and bug bounties could actually find flaws and back-doors in the wallet so the provider doesn’t dare to put these in.
Back-doors and flaws are frequently found in closed source products but some remain hidden for years. And even in open source security software there might be catastrophic flaws undiscovered for years.
An evil wallet provider would certainly prefer not to publish the code, as hiding it makes audits orders of magnitude harder.
For your security, you thus want the code to be available for review.
If the wallet provider doesn’t share up to date code, our analysis stops there as the wallet could steal your funds at any time, and there is no protection except the provider’s word.
“Up to date” strictly means that any instance of the product being updated without the source code being updated counts as closed source. This puts the burden on the provider to always first release the source code before releasing the product’s update. This paragraph is a clarification to our rules following a little poll.
We are not concerned about the license as long as it allows us to perform our analysis. For a security audit, it is not necessary that the provider allows others to use their code for a competing wallet. You should still prefer actual open source licenses as a competing wallet won’t use the code without giving it careful scrutiny.
The product cannot be independently verified. If the provider puts your funds at risk on purpose or by accident, you will probably not know about the issue before people start losing money. If the provider is more criminally inclined he might have collected all the backups of all the wallets, ready to be emptied at the press of a button. The product might have a formidable track record but out of distress or change in management turns out to be evil from some point on, with nobody outside ever knowing before it is too late.Build Verifications
Check your file
Application information
Product Description
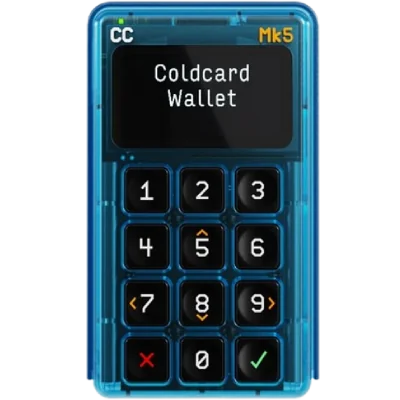
The Coldcard Mk5 is Coinkite’s compact, Bitcoin-only signing device and the successor to the
 Coldcard Mk4 . It was introduced on March 10, 2026. The Mk5 is primarily a physical and usability redesign: Coinkite states that it runs exactly the same firmware image as the Mk4 and that both devices will receive the same firmware updates.
Compared with the Mk4, the Mk5 has a larger 1.54-inch display protected by Gorilla Glass, a redesigned tactile numeric keypad, a bottom-mounted USB-C connector, improved NFC performance, and a tougher case. It has no internal battery and must be continuously powered over USB-C.
Official specifications:
- Size with cover: 87 x 52 x 10.3 mm
- Size without cover: 86 x 50 x 9 mm
- Weight: approximately 55 g
- Power: 65 mA at 5 V over USB-C
- Connectors: USB-C and one MicroSD slot
- 1.54-inch monochrome display protected by Gorilla Glass
- Optional NFC-V communication
- Protective sliding cover
The Mk5 does not have Wi-Fi, Bluetooth, a battery, or a camera. It can display QR codes but cannot scan them. For air-gapped use it can be powered from an AC adapter or battery pack and exchange PSBT files using MicroSD. NFC and USB data are optional interfaces.
Security Model
The Mk5 retains the Mk4 security architecture. It uses secure elements from two manufacturers, Microchip’s ATECC608 family and Maxim’s DS28C36B, together with the main microcontroller to protect the wallet secret. Firmware is checked during startup and the device uses green “Genuine” and red “Caution” LEDs to report the result. Its clear case and numbered, tamper-evident shipping bag are intended to make physical changes easier to notice.
The PIN is entered in two parts. After the prefix, the device displays two device-specific anti-phishing words that the user should recognize before entering the suffix. The secure element permanently disables the device after 13 failed PIN attempts. Optional Trick PINs can open a duress wallet, impose delays, wipe the seed, or brick the device.
The firmware supports BIP-39 seed words and passphrases, encrypted MicroSD backups, temporary seeds, Seed Vault, Seed XOR, BIP-85-derived entropy, single-signature and multisignature wallets, PSBT signing, spending policies, and WIF Store. Compatible coordinator software includes Sparrow, Nunchuk, Bitcoin Core, Electrum, BlueWallet, Specter Desktop, Wasabi, and other listed coordinators. Coinkite says other wallets following the BIP-174/PSBT standards should also be compatible.
Hierarchically Deterministic
All accounts and keys are derived from one masterseed as defined in BIP 32, BIP 39, BIP 44, BIP 49, BIP 84 and BIP 86. While some wallets might use different definitions and not all support SegWit or Taproot, we only consider this feature as given if
- the backup is a BIP 39 mnemonic
- the funds are recoverable on a competitor’s product correctly implementing those standards
- no address reuse
- simple backup
- no vendor lock-in
Why we list it for this wallet
the 24-word seed phrase for your BIP39 wallet
Source: Mk5 product page
Multi Signature
Bitcoin allows to define addresses controlled by more than one private key. Two-of-three for example would mean that any two of a list of three private keys would be required to send coins from this address.
With keys from distinct devices or users, an attacker would have to compromise multiple devices or users at once. Multi signature thus allows to protect against one device catching a virus, one wallet having a backdoor (if the multi signature works across different providers’ wallets), one hardware wallet not being trusted (if hardware wallets can be used for multi signature), etc.
- There are no good standards yet for multi signature accounts. This might mean that an account that works with one provider’s wallet won’t load in any other wallet which can complicate recovery should that wallet go out of business.
- Using Multi Signature results in bigger and thus more expensive transactions.
- Using Multi Signature accounts makes it easier for blockchain analysis companies to follow the trail of a wallet.
- Multi Signature accounts require backups of additional descriptors, making financial loss from user error more likely.
Why we list it for this wallet
Expanded multisig capabilities: handle bigger, more complex transactions.
Source: Mk5 compared to Mk4
NFC (Near Field Communication)
The wallet supports Near Field Communication (NFC) for wireless interaction with hardware wallets, payment terminals, or signing cards. NFC enables tap-to-sign or tap-to-pay functionality over a very short range (typically a few centimeters) without cables or QR codes.
- Convenience: Quick tap interaction — no cables to connect or QR codes to scan.
- Hardware wallet compatibility: Some hardware signing cards communicate exclusively via NFC.
- Requires NFC hardware on both devices.
- Very short range limits usability compared to QR-based air-gapped setups.
Why we list it for this wallet
NFC-V compatible: tap to transmit all data types, including PSBTs, addresses, and XPUBs.
Source: Mk5 compared to Mk4
Secure Elements
Secure Elements in Bitcoin wallets refer to dedicated hardware components designed to enhance security. These elements are specialized circuits or chips embedded in the device, providing a fortified environment for storing sensitive data such as private keys. Unlike standard storage, Secure Elements are resistant to tampering and physical attacks, making them an ideal choice for safeguarding cryptographic data and operations. The use of Secure Elements is crucial, especially in hardware and mobile wallets, where the risk of physical theft or tampering is a concern. These elements can effectively shield private keys from a wide range of attacks, including sophisticated ones like side-channel attacks. They ensure that private keys never leave the secure environment, even when signing transactions, offering a higher level of security compared to software-only solutions. While adding a significant layer of security, Secure Elements may pose challenges in terms of wallet recovery. In cases where the device is damaged or lost, retrieving the private keys can be more complex compared to wallets that solely use software-based security measures.
- Enhanced security against physical and sophisticated attacks
- Increased protection for private keys and sensitive data
- Peace of mind knowing that cryptographic operations are performed in a secure, isolated environment
Potential complexities in wallet recovery and dependency on specific hardware.
Why we list it for this wallet
COLDCARD uses two Secure Elements, from different vendors, to protect your Bitcoin.
Source: Mk5 product page
Firmware and Reproducibility
Coinkite distributes the same signed, timestamped *-mk-coldcard.dfu artifact for Mk4 and Mk5. Its official header declares hw_compat: 0x28, meaning Mk4+Mk5, and the public repository uses MK-Makefile to build the shared firmware. The local reproducibility reports found the firmware payload byte-identical outside the 128-byte header excluded by Coinkite’s comparison method; that header was inspected separately, not reproduced. Consequently, a reproducibility result for a shared Mk firmware artifact applies to both physical products; a separate Mk5 build is not required.
The first official shared Mk4/Mk5 release was version 5.5.0. Older mk4-coldcard.dfu files in the 5.4.x series were released for Mk4 only and do not apply to Mk5. Standard versions 5.5.0 and 5.5.1 and Edge version 6.5.0X were affected by the seed-generation vulnerability described above. Standard 5.6.0 and Edge 6.6.0X correct new seed generation.
The firmware source is publicly available and Coinkite provides a reproducible-build procedure. However, the repository applies the Commons Clause, which removes permission to sell products or services whose value substantially derives from the software. It is therefore classified here as source available, rather than free and open-source software.
Product page updated by Daniel Andrei R. Garcia
Community Opinions
These comments are contributed by Nostr users.
Loading opinions…
Do your own research
In addition to reading our analysis, it is important to do your own checks. Before transferring any bitcoin to your wallet, look up reviews for the wallet you want to use. They should be easy to find. If they aren't, that itself is a reason to be extra careful.