Passed 8 of 10 tests
We check each wallet from its code to the app on your device, asking these questions in order:
We stopped asking questions after we encountered a failed answer.
The answer is "yes".
If the answer were "no", we would mark it as "Fake" and the following would apply:
The answer is "no". We marked it as "Fake".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Fake" and the following would apply:
The bigger wallets often get imitated by scammers that abuse the reputation of the product by imitating its name, logo or both.
Imitating a competitor is a huge red flag and we urge you to not put any money into this product!
The answer is "yes".
If the answer were "no", we would mark it as "Announced but never delivered" and the following would apply:
The answer is "no". We marked it as "Announced but never delivered".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Announced but never delivered" and the following would apply:
Some products are promoted with great fund raising, marketing and ICOs, to disappear from one day to the other a week later or they are one-man side projects that get refined for months or even years to still never materialize in an actual product. Regardless, those are projects we consider “vaporware”.
The answer is "yes".
If the answer were "no", we would mark it as "Un-Released" and the following would apply:
The answer is "no". We marked it as "Un-Released".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Un-Released" and the following would apply:
We focus on products that have the biggest impact if things go wrong and while pre-sales sometimes reach many thousands to buy into promises that never materialize, the damage is limited and there would be little definite to be said about an unreleased product anyway.
If you find a product in this category that was released meanwhile, please contact us to do a proper review!
The answer is "yes".
If the answer were "no", we would mark it as "Not a wallet" and the following would apply:
The answer is "no". We marked it as "Not a wallet".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Not a wallet" and the following would apply:
If it’s called “wallet” but is actually only a portfolio tracker, we don’t look any deeper, assuming it is not meant to control funds. What has no funds, can’t lose your coins. It might still leak your financial history!
If you can buy Bitcoins with this app but only into another wallet, it’s not a wallet itself.
The same goes for off-ramps that hold no balance at all: bitcoin (or gift cards) go in and fiat goes straight out to your bank. An off-ramp that keeps your fiat until you cash out is a wallet, just not for Bitcoin. One that keeps a bitcoin balance you can’t send out is ‘Can’t send or receive bitcoins’.
The answer is "yes".
If the answer were "no", we would mark it as "A wallet but not for Bitcoin" and the following would apply:
The answer is "no". We marked it as "A wallet but not for Bitcoin".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "A wallet but not for Bitcoin" and the following would apply:
At this point we only look into wallets that at least also support BTC.
A product that can send and receive other coins but only tracks Bitcoin addresses read-only is a wallet, just not for Bitcoin, so it gets this verdict. ‘Not a wallet’ is for products that hold no coins at all, such as pure portfolio trackers.
The same goes for off-ramps that credit your bitcoin to a fiat balance you later cash out: the app holds your money, but not as bitcoin.
The answer is "yes".
If the answer were "no", we would mark it as "Provided private keys" and the following would apply:
The answer is "no". We marked it as "Provided private keys".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Provided private keys" and the following would apply:
The best hardware wallet cannot guarantee that the provider deleted the keys if the private keys were put onto the device by them in the first place.
There is no way of knowing if the provider took a copy in the process. If they did, all funds controlled by those devices are potentially also under the control of the provider and could be moved out of the client’s control at any time at the provider’s discretion.
The product cannot be independently verified. If the provider puts your funds at risk on purpose or by accident, you will probably not know about the issue before people start losing money. If the provider is more criminally inclined he might have collected all the backups of all the wallets, ready to be emptied at the press of a button. The product might have a formidable track record but out of distress or change in management turns out to be evil from some point on, with nobody outside ever knowing before it is too late. The answer is "yes".
If the answer were "no", we would mark it as "Leaks Keys" and the following would apply:
The answer is "no". We marked it as "Leaks Keys".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Leaks Keys" and the following would apply:
Some people claim their paper wallet is a hardware wallet. Others use RFID chips with the private keys on them. A very crucial drawback of those systems is that in order to send a transaction, the private key has to be brought onto a different system that doesn’t necessarily share all the desired aspects of a hardware wallet.
Paper wallets need to be printed, exposing the keys to the PC and the printer even before sending funds to it.
Simple RFID based devices can’t sign transactions - they share the keys with whoever asked to use them for whatever they please.
There are even products that are perfectly capable of working in an air-gapped fashion but they still expose the keys to connected devices.
This verdict is reserved for key leakage under normal operation and does not apply to devices where a hack is known to be possible with special hardware.
The product cannot be independently verified. If the provider puts your funds at risk on purpose or by accident, you will probably not know about the issue before people start losing money. If the provider is more criminally inclined he might have collected all the backups of all the wallets, ready to be emptied at the press of a button. The product might have a formidable track record but out of distress or change in management turns out to be evil from some point on, with nobody outside ever knowing before it is too late. The answer is "yes".
If the answer were "no", we would mark it as "Bad Interface" and the following would apply:
The answer is "no". We marked it as "Bad Interface".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "Bad Interface" and the following would apply:
These are devices that might generate secure private key material, outside the reach of the provider but that do not have the means to let the user verify transactions on the device itself. This verdict includes screen-less smart cards or USB-dongles.
The wallet lacks either a screen or buttons or both. In consequence, crucial elements of approving transactions is being delegated to other hardware such as a general purpose PC or phone which defeats the purpose of a hardware wallet. For big exit scams, a companion app could always request two signatures - one for the coffee you are paying and a second to empty your wallet completely. The former could be broadcast while the latter only gets collected for later use.
Another consquence of a missing screen is that the user is faced with the dilemma of either not making a backup or having to pass the backup through an insecure device for display or storage.
The software of the device might be perfect but this device cannot be recommended due to this fundamental flaw.
The product cannot be independently verified. If the provider puts your funds at risk on purpose or by accident, you will probably not know about the issue before people start losing money. If the provider is more criminally inclined he might have collected all the backups of all the wallets, ready to be emptied at the press of a button. The product might have a formidable track record but out of distress or change in management turns out to be evil from some point on, with nobody outside ever knowing before it is too late. The answer is "yes".
If the answer were "no", we would mark it as "No source for current release found" and the following would apply:
The answer is "no". We marked it as "No source for current release found".
We did not ask this question because we failed at a previous question.
If the answer were "no", we would mark it as "No source for current release found" and the following would apply:
A wallet that claims to not give the provider the means to steal the users’ funds might actually be lying. In the spirit of “Don’t trust - verify!” you don’t want to take the provider at his word, but trust that people hunting for fame and bug bounties could actually find flaws and back-doors in the wallet so the provider doesn’t dare to put these in.
Back-doors and flaws are frequently found in closed source products but some remain hidden for years. And even in open source security software there might be catastrophic flaws undiscovered for years.
An evil wallet provider would certainly prefer not to publish the code, as hiding it makes audits orders of magnitude harder.
For your security, you thus want the code to be available for review.
If the wallet provider doesn’t share up to date code, our analysis stops there as the wallet could steal your funds at any time, and there is no protection except the provider’s word.
“Up to date” strictly means that any instance of the product being updated without the source code being updated counts as closed source. This puts the burden on the provider to always first release the source code before releasing the product’s update. This paragraph is a clarification to our rules following a little poll.
We are not concerned about the license as long as it allows us to perform our analysis. For a security audit, it is not necessary that the provider allows others to use their code for a competing wallet. You should still prefer actual open source licenses as a competing wallet won’t use the code without giving it careful scrutiny.
The product cannot be independently verified. If the provider puts your funds at risk on purpose or by accident, you will probably not know about the issue before people start losing money. If the provider is more criminally inclined he might have collected all the backups of all the wallets, ready to be emptied at the press of a button. The product might have a formidable track record but out of distress or change in management turns out to be evil from some point on, with nobody outside ever knowing before it is too late.Build Verifications
Build cannot be done because the source code is not publicly available.Application information
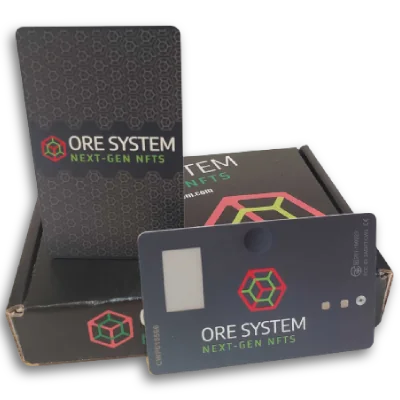
Update 2026-10-30: ORE System no longer sells this card. Its website only shows a “Coming Soon” page, and has done so since at least November 2023. The card is a co-branded CoolWallet Pro, so existing cards still work with the CoolWallet app. We mark it as discontinued.
Update 2024-12-08: This product remains available and not verifiable.
Background Information
The ORE System is a next-generation block-chain technology that creates value for content-creators, collectors, and studios.
ORE System specializes in blockchain enabled gaming and integration. The ORE System is a single ecoverse including The ORE Token, The ORE SDK, The ORE Forge and The ORE Stealth.
The ORE System card is a co-branding effort with:
Interested users can find more information about their co-branding partnership on this page.
Product Description
As a co-branded device with
 CoolWallet Pro , we believe that it possesses the same characteristics - including the price.
- Encrypted Bluetooth connection for Android and iOS
- EAL 6+ certified Secure Element
- DeFi, Dapp and NFT (e.g. Rarible, Opensea) In-app Integration Coming Soon
- Multi-cryptocurrency Support
- Trading features
- Staking
- Tron (TRX), Cosmos (ATOM), PolkaDot (DOT), BEP20 Token- BNB, BEP20 Official and Customized Tokens, TRC20 Tokens – USDT / USDJ / JUST / WBTT / WIN & All Other TRC20 Tokens
- Bitcoin Specification Supported
- Bitcoin algorithm: Support transaction signing algorithm ECDSA with specified elliptic curve secp256k1
- BIP-32 : BIP-32 HD Wallets
- BIP-44 : BIP-44 Support multiple coin type and accounts. Each account includes up to 232 external and internal Bitcoin transaction addresses
- Seed Generation
- Generate seed directly from the CoolWallet Pro (recommended) or via the CoolBitX Crypto App.
Analysis
The unboxing video from ORE System shows a CoolWallet Pro box. But the card inside shows the branding of the ORE System.
As indicated in the
CoolWallet Pro review, the firmware is not publicly available.
We’d like to add that the device pairs with a mobile app. We’ve asked ORE System via Telegram whether their device pairs with the following apps or if they have their own:
- Android CoolWallet
- iPhone CoolWallet
CoolBitX (the manufacturer of the CoolWalletPro) disclosed in December 18, 2020, that the device has a vulnerability related to its Bluetooth pairing. The vulnerability exists given the following conditions:
- If a user uses the basic wallet creation and wallet recovery functions through an outdated app version.
- If a malicious actor is physically within 30 meters of you and your CoolWallet at that time.
- If the bad actor has prepared a second CoolWallet to intercept private information.
This has since been patched. The url for this article describes this as a “Seed Replay Attack”, which can only be executed provided the 3 conditions above are met.
While the Javascript SDK for the CoolWallet Pro is available on their GitHub repositories, we were not able to find the firmware’s repository.
Secure Elements
Secure Elements in Bitcoin wallets refer to dedicated hardware components designed to enhance security. These elements are specialized circuits or chips embedded in the device, providing a fortified environment for storing sensitive data such as private keys. Unlike standard storage, Secure Elements are resistant to tampering and physical attacks, making them an ideal choice for safeguarding cryptographic data and operations. The use of Secure Elements is crucial, especially in hardware and mobile wallets, where the risk of physical theft or tampering is a concern. These elements can effectively shield private keys from a wide range of attacks, including sophisticated ones like side-channel attacks. They ensure that private keys never leave the secure environment, even when signing transactions, offering a higher level of security compared to software-only solutions. While adding a significant layer of security, Secure Elements may pose challenges in terms of wallet recovery. In cases where the device is damaged or lost, retrieving the private keys can be more complex compared to wallets that solely use software-based security measures.
- Enhanced security against physical and sophisticated attacks
- Increased protection for private keys and sensitive data
- Peace of mind knowing that cryptographic operations are performed in a secure, isolated environment
Potential complexities in wallet recovery and dependency on specific hardware.
Why we list it for this wallet
EAL 6+ certified Secure Element
Source: Product Description
Hierarchically Deterministic
All accounts and keys are derived from one masterseed as defined in BIP 32, BIP 39, BIP 44, BIP 49, BIP 84 and BIP 86. While some wallets might use different definitions and not all support SegWit or Taproot, we only consider this feature as given if
- the backup is a BIP 39 mnemonic
- the funds are recoverable on a competitor’s product correctly implementing those standards
- no address reuse
- simple backup
- no vendor lock-in
Why we list it for this wallet
BIP-32 : BIP-32 HD Wallets
Source: Product Description
Unlimited Accounts
The user can create or restore secondary BTC accounts
- Accounting: Multiple accounts allow for easier separation of funds.
- Privacy: Using an account with a positive balance at all time makes it relatively easy for blockchain analysis companies to determine the full history of the wallet. By using multiple accounts, emptying them at times, the user can retain some privacy.
Why we list it for this wallet
BIP-44 : BIP-44 Support multiple coin type and accounts. Each account includes up to 232 external and internal Bitcoin transaction addresses
Source: Product Description
Product page updated by Daniel Andrei R. Garcia
Community Opinions
These comments are contributed by Nostr users.
Loading opinions…
Do your own research
In addition to reading our analysis, it is important to do your own checks. Before transferring any bitcoin to your wallet, look up reviews for the wallet you want to use. They should be easy to find. If they aren't, that itself is a reason to be extra careful.